Encrypt and decrypt against the Cloud KMS API. Not a security boundary.
Key rings, keys and versions over gRPC and JSON: symmetric, asymmetric and MAC. Key material is stored unencrypted.
Backed by: CloudBurrow CloudBurrow
Get startedWhat it covers
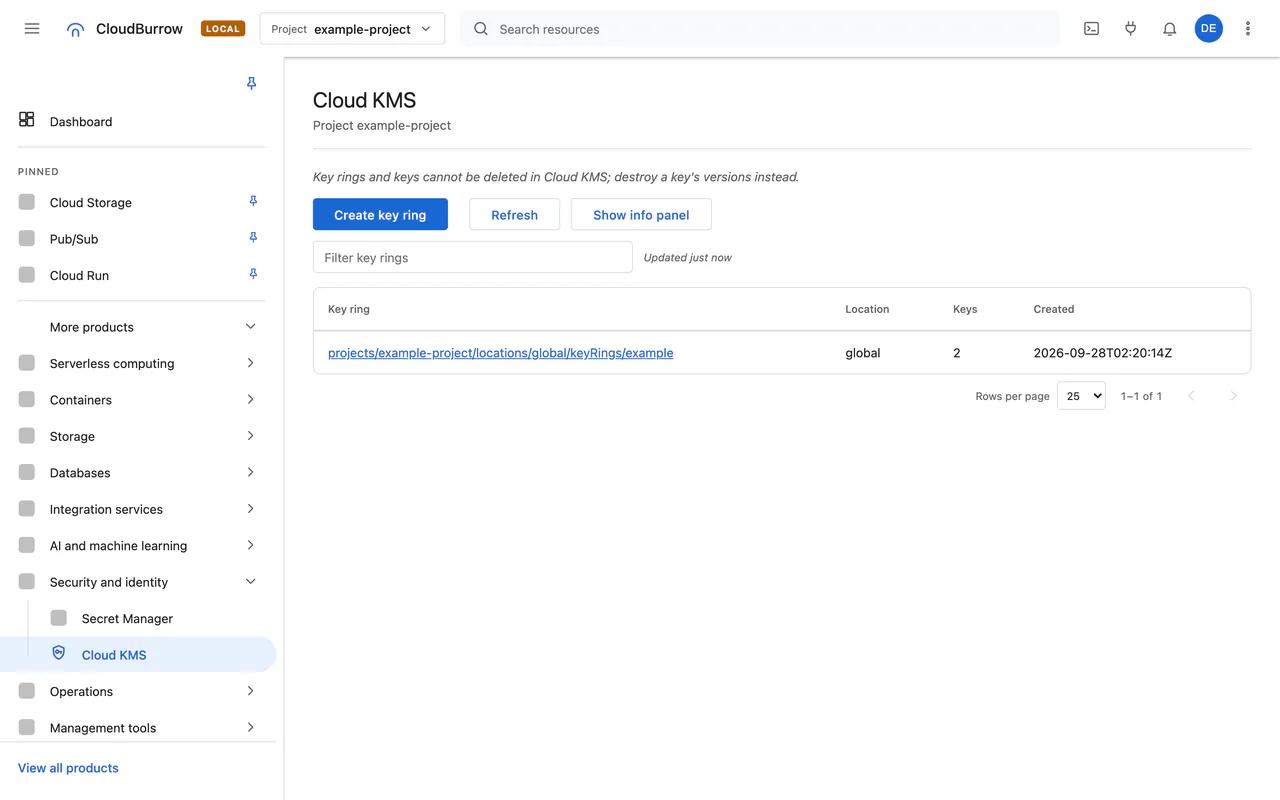
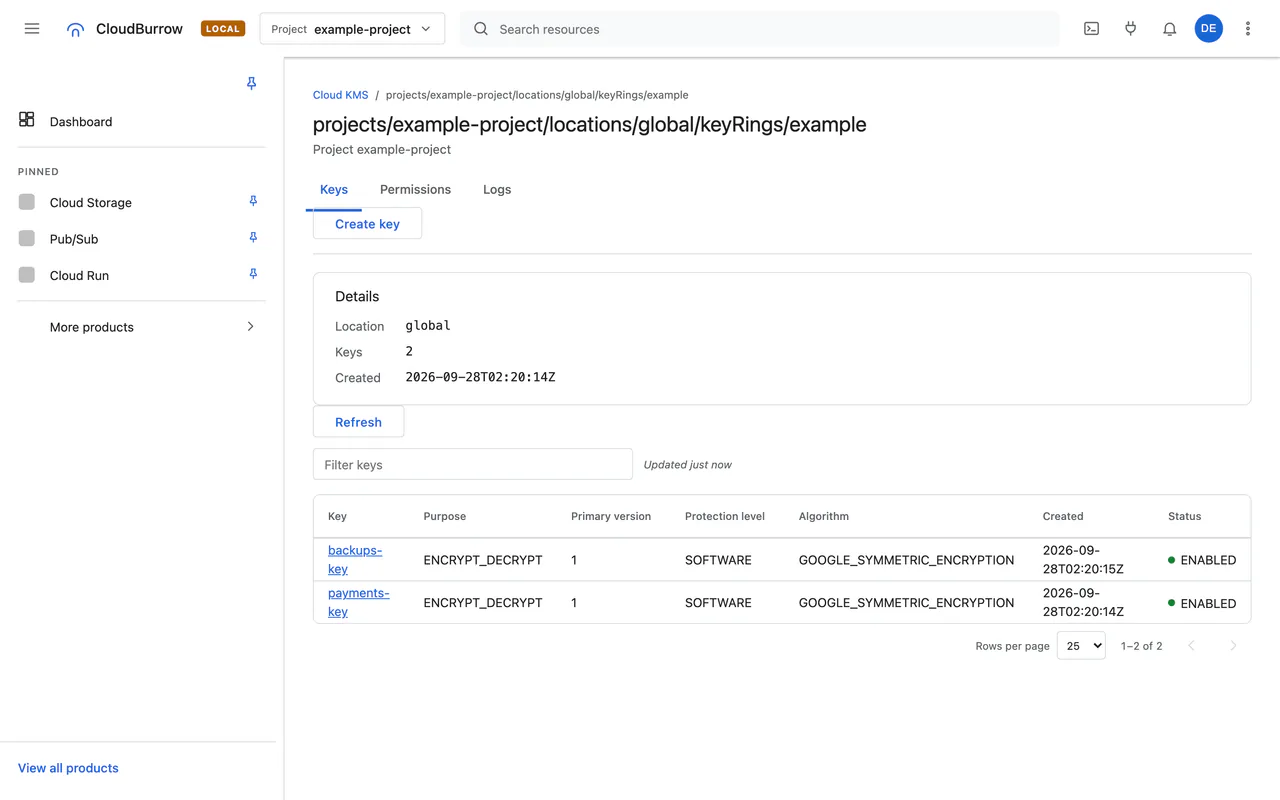
Cloud KMS is built by CloudBurrow, because Google publishes no emulator for it, and starts with --services kms. It serves symmetric, asymmetric and MAC keys, Encrypt and Decrypt, signing and the version lifecycle, with named client tests for each, and local key-management metadata. It is not a security boundary: key material is stored unencrypted.
- Key rings, symmetric keys and versions
- Encrypt and Decrypt over gRPC and JSON
- The version lifecycle: enable, disable, destroy and restore
- Automatic key rotation (#816)
- Tink with tink-go-gcpkms Verified
- Asymmetric signing and decryption, MAC, raw symmetric and key encapsulation keys, and import jobs (#1212)
- Local HSM, EKM and Autokey API surfaces with documented limits
-
gcloud kmsand Terraform for key rings, keys, versions and IAM policies
In the console
What's verified
Follow the operation matrix to see what the backend serves and the tests linked to Verified calls.
Not supported
- 01 / Local boundary
Not a security boundary: key material is stored unencrypted
- 02 / Local boundary
IAM policies on key rings and keys are stored, never enforced #428
- 03 / Local boundary
HSM and EKM keys are served with no real HSM or external key manager behind them: this instance acts as both.
Source: docs/compatibility.md at main 0ea2594.
Questions
Is it safe for real keys?
Build against Google Cloud APIs, locally
Free and open source under Apache-2.0. No account, no sign-up, no Google Cloud bill.